GitHub Agentic Workflows is now generally available
GitHub Agentic Workflows runs coding agents inside GitHub Actions to automate tasks like issue triage and CI failure analysis. It became generally available on October 28, 2026.
If you maintain repositories, this announcement means you need to decide which repetitive jobs to hand to AI, and how much permission to give it. It is like handing work to a person: you write a manual and set up an approval chain. With Agentic Workflows, you describe the task in plain text, the AI reads it and does the work, and results reach the repository only through a defined process. Even with an approval chain, results depend on how you write the manual, so your team still has to decide what to delegate.
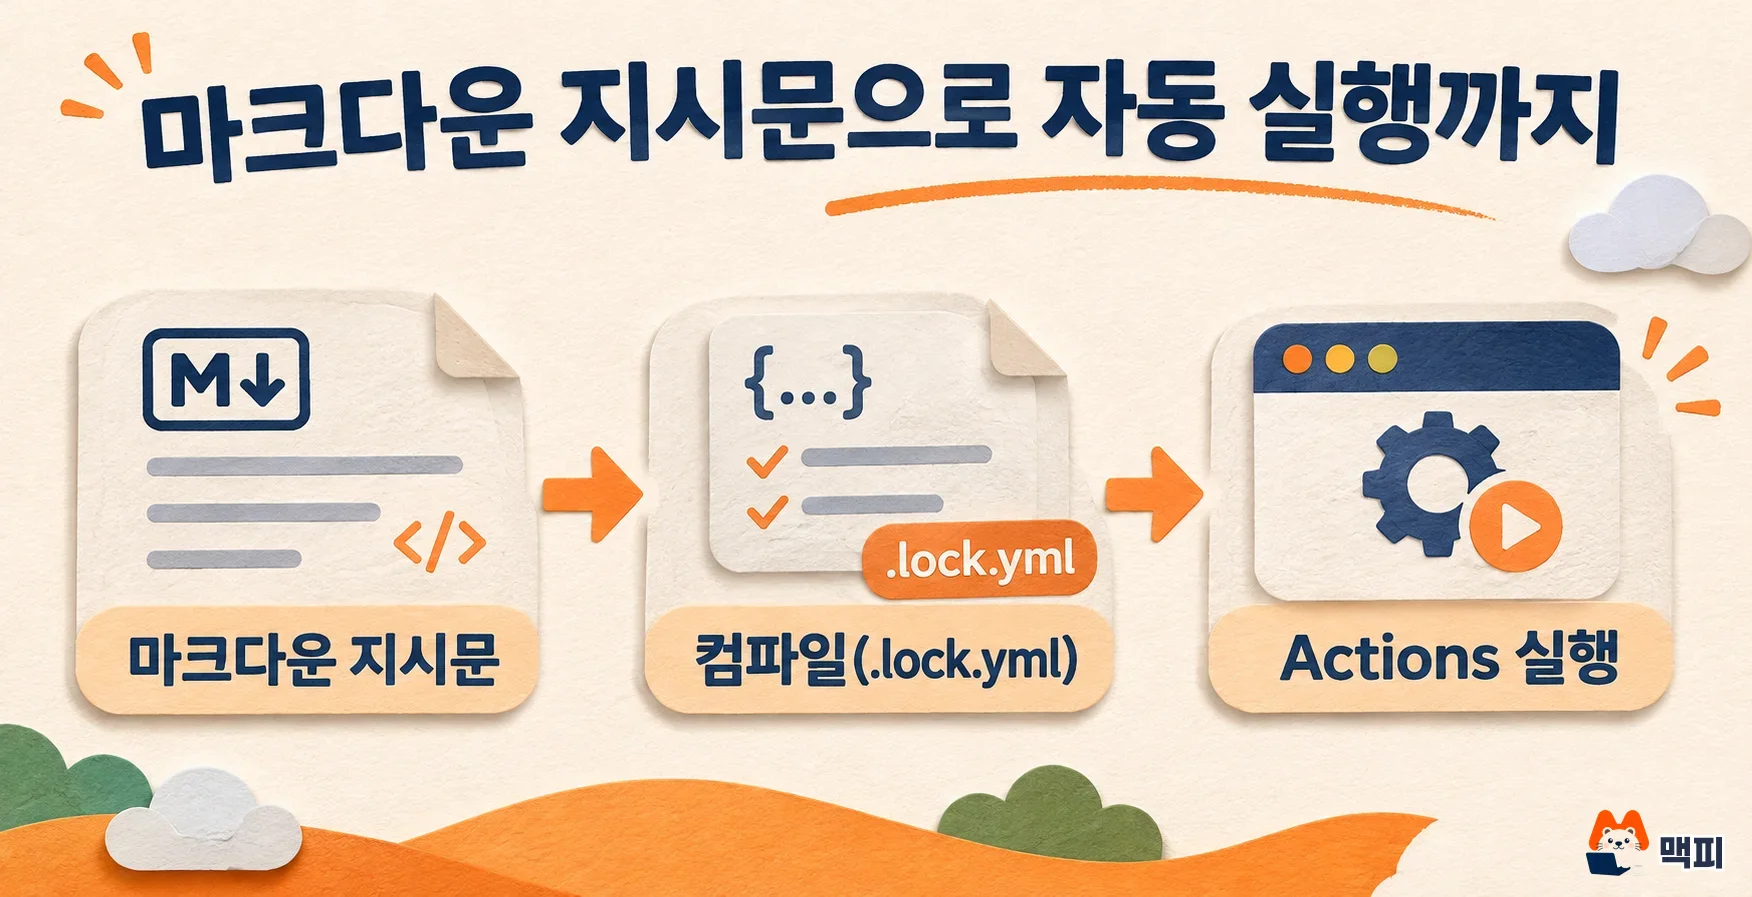
According to the official GitHub changelog, this feature is an open-source project from GitHub Next. It automates tasks that need reasoning, such as issue triage, CI failure analysis, documentation updates, and test writing. You write the automation as a natural-language Markdown file. It compiles to standard Actions YAML, so your existing runner groups and policy constraints still apply.
What changed Agentic Workflows moved from preview to general availability. ARC runner support, budget forecasting, model routing, and stronger isolation were added.
Who is affected Teams with Free, Team, or Enterprise repositories on github.com who want to automate repetitive work like issue triage or CI checks.
What to do now Run one example workflow from the quickstart in a repository where you have write access, then check the cost forecast with gh aw forecast.
What changed since the preview
According to GitHub's announcement, five things changed after the preview.
| Area | What changed |
|---|---|
| Runners | Support for self-hosted ARC (Actions Runner Controller, a tool that manages runners on Kubernetes) runners and Docker-in-Docker |
| Cost forecast | gh aw forecast is no longer experimental and shows AI credit spend, including threat detection credits and a monthly range |
| Models and engines | Updated model list, per-workflow model provider choice, and new templates added with gh aw add-wizard |
| Model routing | A router can pick the model that fits the task type and difficulty |
| Isolation | Agents run in Cloud Hypervisor or NVX micro VMs, with an enclave that blocks data leaks between repositories |
According to the official announcement, the default engine is GitHub Copilot CLI, so you need a Copilot license to use it. You can also bring another coding agent. It is offered on GitHub Free, Team, and Enterprise on github.com. The announcement has no separate price list. It only tells you to estimate cost with gh aw forecast. For Copilot billing, see GitHub Copilot code review pricing and organization billing settings.
How Agentic Workflows run safely
According to the official architecture docs, the Markdown file becomes a .lock.yml at the compile step. Along the way it goes through schema validation, action SHA pinning, and checks by security scanners such as actionlint, zizmor, and poutine. If a check fails, compilation fails.
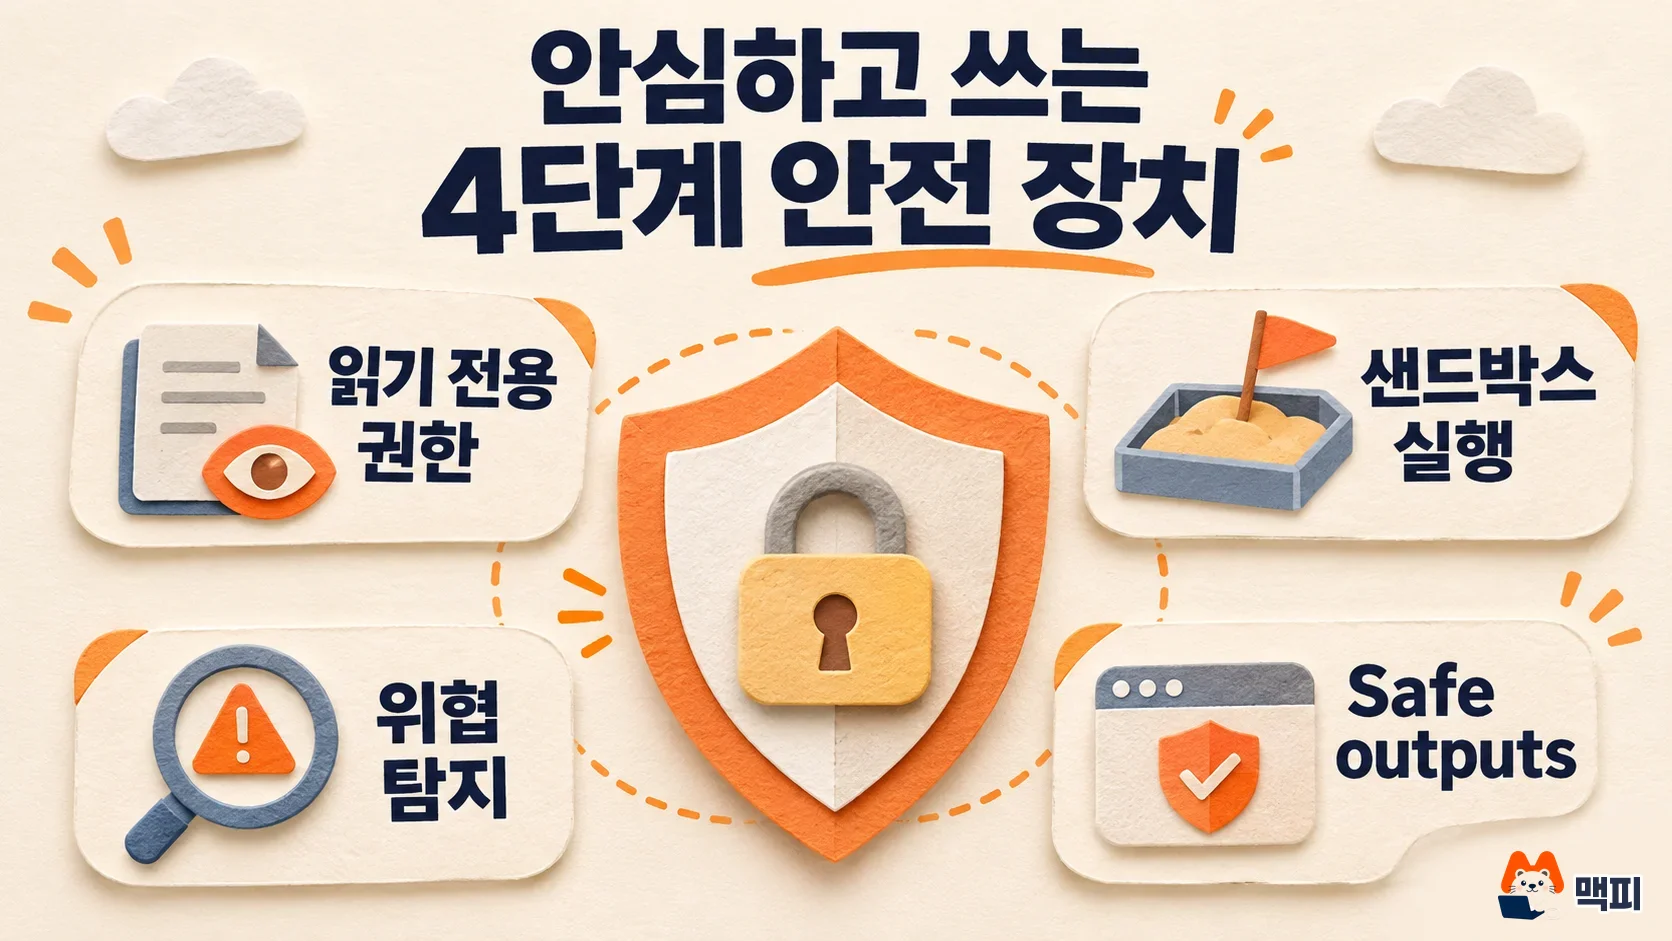
The AI agent job runs with minimal read-only permissions. Write actions such as creating an issue or a PR do not run directly. They are stored as output files. A separate job takes these outputs and first scans for leaked secrets or malicious patches. Only what passes is applied, with tightly scoped write permissions. In the default warning mode, if a threat is detected, the output gets a comment or is turned into a PR for review. In strict mode, it blocks the change and fails the workflow. The docs state that detection is only one layer of defense and does not prove safety.
The security features GitHub highlights are integrity filtering (rules applied when the agent accesses GitHub content), read-only permissions by default, a sandboxed container behind the Agent Workflow Firewall, Safe outputs validation, and threat detection jobs.
You can use it in your own repositories
According to the official announcement, it covers the Free, Team, and Enterprise plans on github.com. To use the default engine, you need a Copilot license. If you bring another engine, you need an account for that engine. The quickstart lists these prerequisites.
- AI account: one of GitHub Copilot, Anthropic Claude, OpenAI Codex, or Google Gemini
- A repository where you have write access, with GitHub Actions turned on
- GitHub CLI (
gh) v2.0.0 or later, running on Linux, macOS, or Windows with WSL
Secret names differ by engine. Copilot uses COPILOT_GITHUB_TOKEN, Claude uses ANTHROPIC_API_KEY, Codex uses OPENAI_API_KEY, and Gemini uses GEMINI_API_KEY. The docs say CLAUDE_CODE_OAUTH_TOKEN is not supported for Claude.
What to do now: run the example workflow
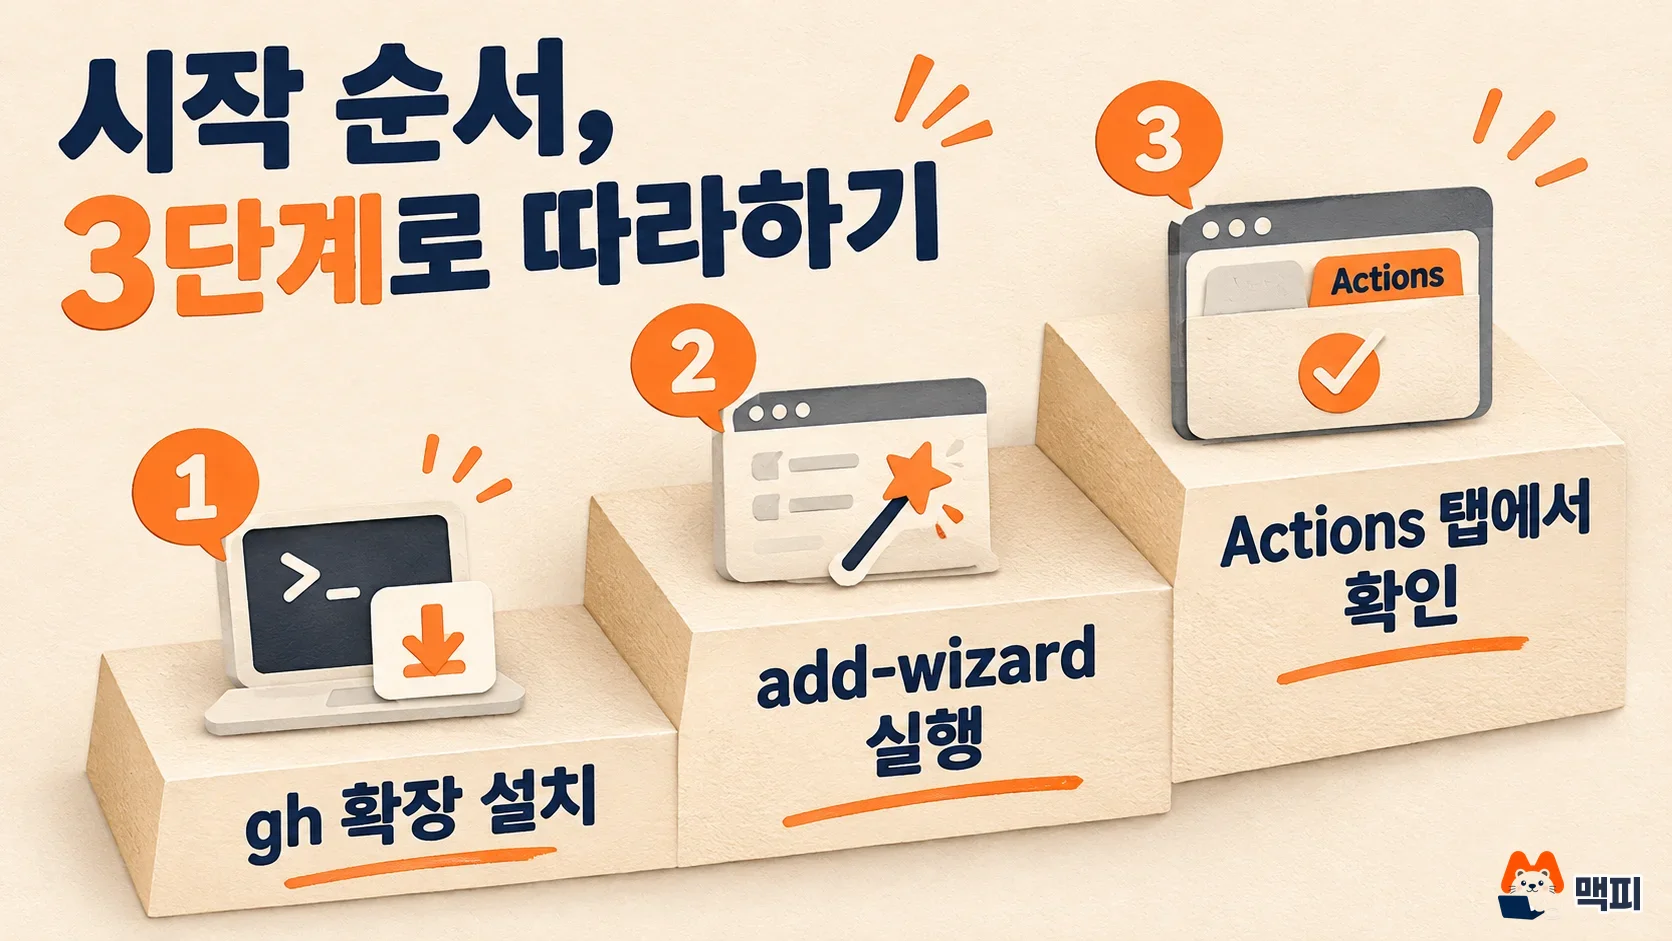
The first-run steps in the official quickstart are as follows.
- Install the extension with
gh extension install github/gh-aw. - From the repository root, run
gh aw add-wizard githubnext/agentics/repo-status. The wizard walks you through permission checks, AI engine choice, authentication setup, adding the workflow file (direct push or PR), and the first run. - Open the latest run in the Actions tab, or check the status with
gh aw status.
If it works, an issue titled "Daily Repo Report" appears in your repository. If it fails, check the step-by-step logs in Actions. To change the content, edit .github/workflows/repo-status.md. If you changed the frontmatter settings, run gh aw compile, then commit both the .md and .lock.yml files together. To run it again, use gh aw run repo-status. Examples for issue triage, dependency management, code review, and reporting are in the agentics repository.
If cost is a concern, check the AI credit spend forecast from gh aw forecast first. The official announcement says it includes threat detection credits and a monthly range.
What to watch next
The announcement has no pricing structure, so watch the official changelog and the release notes for updates. In this announcement, GitHub highlighted a case where a team lead at Accenture said they saved about 29 hours a week on personal development work. Keep in mind that this figure is based on one person's own work. For detailed usage, see the official docs.
Frequently asked questions
Do I need to change my existing GitHub Actions workflows?
The announcement explains that Agentic Workflows compiles Markdown to standard Actions YAML and keeps using your existing runner groups and policy constraints. It gives no instruction to change existing workflows.
Can I use it without Copilot?
Yes. According to the quickstart, the default engine, Copilot CLI, needs a Copilot license. But you can use another engine with a Claude, Codex, or Gemini account and the matching secret.
Will the AI change my code on its own?
The architecture docs explain that the agent job is read-only. Writes are done only by the safe output job, within a limited scope, after the detection job.
Found this useful? Share it
Latest posts
Kakao Share Thumbnail Not Showing? Here's the Fix (JavaScript SDK 2025)
Learn why Kakao Share thumbnails don't appear even with a valid imageUrl, and fix it using scrapImage to convert your URL into a KAGE CDN URL. Step-by-step guide.
How to Generate CRM User Manuals in 20 Minutes with Claude Code Sub-Agents
Learn how Claude Code sub-agents can analyze your CRM codebase and auto-generate user manuals and visual guidebooks in just 20 minutes. See the real-world results.
GEO Generative Engine Optimization: The Complete 2025 AI Marketing Strategy Guide
Learn what GEO (Generative Engine Optimization) is, how it differs from traditional SEO, and discover 5 proven AI marketing strategies to get cited by AI search engines in 2025.
Related projects
Get new posts by email
Insights on marketing, analytics, and dev, delivered to your inbox.