The Claude Admin API user sign-out is a beta feature added on November 5, 2026. With one API request, a Claude Enterprise admin can end one employee's login on every browser and device. When someone leaves the company or loses a laptop, security teams need to decide again whether they can cut off the login without deleting the account. It works like a hotel front desk that voids a lost key card and issues a new one. The card stops working, but the desk does not clear out the luggage left in the room. In the same way, this request splits what it cuts off from what stays.
What changed On November 5, 2026, Anthropic added a beta Admin API endpoint that signs Claude Enterprise members out of all devices.
Who is affected Security and IT admins of Claude Enterprise (claude.ai) organizations. Claude Platform organizations that use only the API are not covered.
What to do now Prepare an Admin API key with the write:members scope, and add both the sign-out request and API key deletion to your offboarding and lost-device procedures.
Claude Admin API user sign-out: what changed
In the November 5 entry of the Claude Platform release notes, Anthropic released a sign-out endpoint for Claude Enterprise members in beta. The endpoint is POST /v1/organizations/users/{user_id}/sign_out. According to the user management docs, it signs a member out of every browser and device without removing them from the organization.
The request has no body and needs three headers. Put the admin key in x-api-key, the API version in anthropic-version, and the beta value admin-user-sign-out-2026-10-08 in anthropic-beta. Without the beta header you get a 400 error. On success you get a 200 with that member's details, and values such as the role stay the same.
How to send the Claude Admin API sign-out request
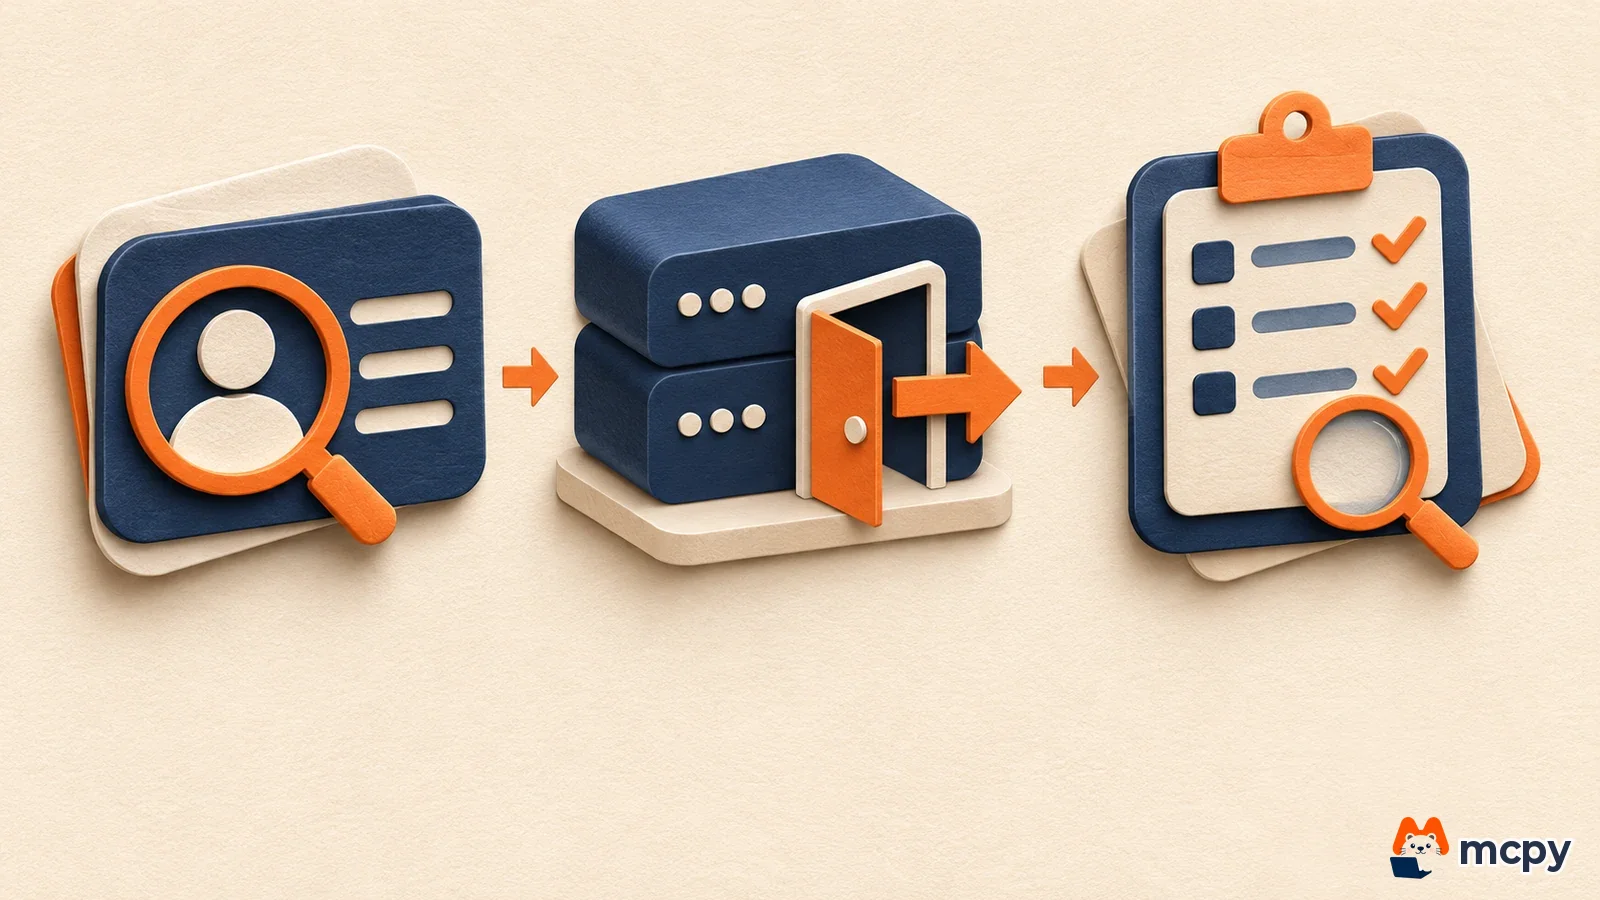
- In the API section of your claude.ai organization settings, create an Admin API key with the
write:membersscope. According to the user management docs, each connected organization needs its own key, created by that organization's Primary owner. To find a member by email, also selectread:members. - Use List users to query
/v1/organizations/users?email=jane@example.comand get theidthat starts withuser_. Email matching ignores case and also catches variants such asjane+hiring@example.com, so check that the name and email belong to the right person. - Send
POST /v1/organizations/users/{user_id}/sign_outwith the headers above. - When a 200 comes back, follow the verification steps below and check that the audit log has a record.
Before using it in production, we recommend a trial run with a test member account. Log that account in to claude.ai and Claude Code, send the request, and check that both ask for a new login and that the audit log has a record. As the official docs warn, tokens can take up to an hour to stop, so check the apps after some time. The request is safe to send again. It returns 200 even when nothing is left to cut off. If it fails, use the status code to find the cause.
| Status | Meaning |
|---|---|
400 cannot_sign_out_primary_owner | The target is the Primary owner |
400 organization_not_enrolled_in_beta | This beta is not yet open for your organization |
| 403 | The key does not have write:members |
| 404 | No member with that ID exists in the organization |
| 429 | You exceeded the shared Admin API limit (100 per minute). Wait for the retry-after time |
| 503 | A required service is temporarily down. What was already cut off stays cut off, so retry until you get a 200 |
What sign-out cuts off and what stays
The request cuts off three things: all login sessions on that person's account, trusted devices (which must be registered again), and OAuth tokens issued for this organization. Apps such as Claude Code must log in again. The official docs say tokens usually stop right away and at the latest within an hour.
Sessions and trusted devices belong to the personal account, so the person's logins for other organizations and personal plans are also cleared. Only the OAuth tokens are limited to this organization.
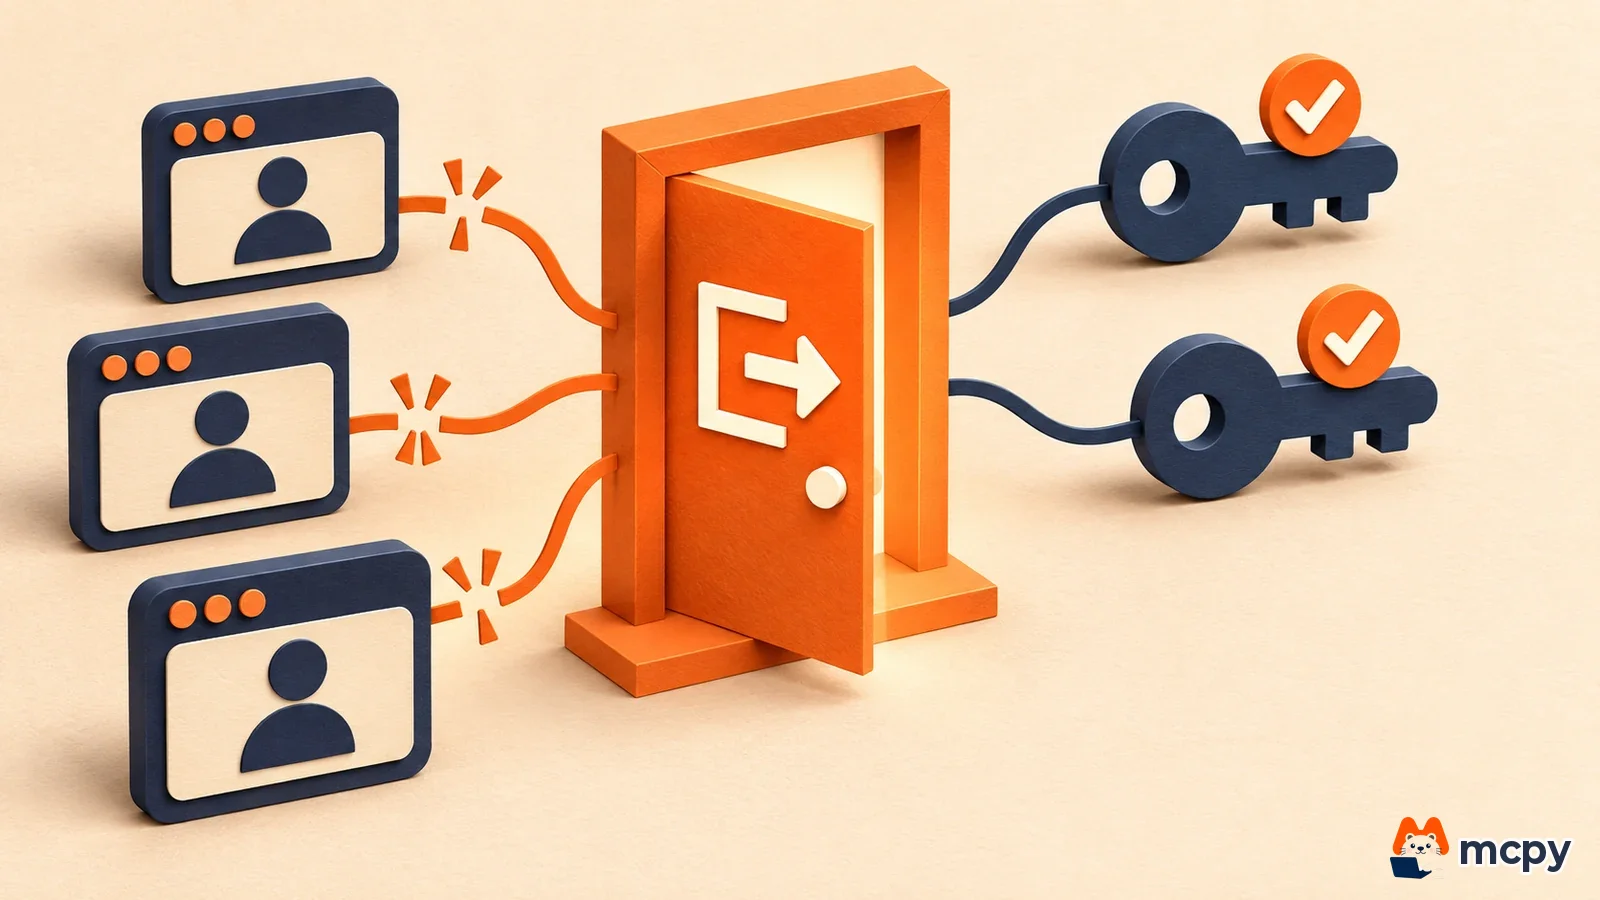
On the other hand, what the docs say is not cut off is listed below.
| What remains | What to do |
|---|---|
| API keys (including Admin API keys the person created) | Delete them yourself under Keys in the API section of claude.ai organization settings |
| OAuth tokens for other organizations | Send a separate request with that organization's key |
| Claude Code cloud sessions and routines | They keep running, and work may fail before it moves to new credentials |
| Computers connected to Cowork | The connection stays |
| Logins in progress | They may finish within up to 5 minutes after the request |
So sign-out alone is not enough if your goal is to lock out a departing employee. The member can sign in again right after sign-out. Use Remove user (DELETE /v1/organizations/users/{user_id}) from the same docs to remove the member, and also deactivate their identity provider (IdP) account. The docs warn that if you only deactivate the account and leave the member in the list, automatic provisioning can add them back at their next login as long as the IdP account is alive. The Primary owner cannot be signed out through this API, so they do it themselves in their claude.ai account settings.
How to check that sign-out worked
Judge success by the records, not by the 200 response. According to the official docs, a completed sign-out appears in the claude.ai audit log export as org_user_trusted_devices_revoked. If you use the Compliance API, the activity feed shows the number of devices and sessions that were cut off. A request that stopped halfway does not appear in the audit log. It shows up in the activity feed with completed set to false. Deleting push notification registrations is asynchronous, so a 200 does not guarantee this step is done.
If the person's login records still appear in the audit log after the request, or they were using an app such as Claude Code at the time, send the same request again after 5 minutes. To see how this fits with other admin features, also read about Claude inference hooks (a feature that blocks prompts before they are sent) and Claude API OpenTelemetry export (a feature that sends usage records to monitoring tools).
What to watch next
According to the release notes, this endpoint is in beta, and some organizations may get an organization_not_enrolled_in_beta error. The beta header value contains a date, so it may change when the feature becomes generally available. If you put it in an operations script, check the release notes regularly. Because this involves employee personal data and access logs, companies in Korea should also set retention and access rights for sign-out request logs in line with their internal policies.
Frequently asked questions
Does signing a user out delete their conversation history or seat?
No. The member stays in the organization, keeps the same role, and can sign in again right away. To get the seat back, you need to use Remove user.
Can I sign someone out if I only know their email?
The sign_out request needs an ID that starts with user_. First look up the ID by passing the email to List users.
Do tokens used in Claude Code stop right away?
The official docs say tokens usually stop right away and at the latest within an hour. Claude Code sessions running in the cloud keep running, so check them separately.
Found this useful? Share it
Latest posts
Kakao Share Thumbnail Not Showing? Here's the Fix (JavaScript SDK 2025)
Learn why Kakao Share thumbnails don't appear even with a valid imageUrl, and fix it using scrapImage to convert your URL into a KAGE CDN URL. Step-by-step guide.
How to Generate CRM User Manuals in 20 Minutes with Claude Code Sub-Agents
Learn how Claude Code sub-agents can analyze your CRM codebase and auto-generate user manuals and visual guidebooks in just 20 minutes. See the real-world results.
GEO Generative Engine Optimization: The Complete 2025 AI Marketing Strategy Guide
Learn what GEO (Generative Engine Optimization) is, how it differs from traditional SEO, and discover 5 proven AI marketing strategies to get cited by AI search engines in 2025.
Related projects
Get new posts by email
Insights on marketing, analytics, and dev, delivered to your inbox.