The Google Cloud IAM helper agent skills are 4 skills that let a coding agent diagnose permission errors, draft least-privilege policies, simulate the impact of changes and request temporary access. Google Cloud announced them on its blog on October 27, 2026. Diagnosis and simulation run automatically, but changes to access policies stop for human approval.
What changed Google Cloud released 4 skills that let agents use IAM (the permission system that decides who can access which resources), plus read-only MCP tools that back them.
Who is affected Developers and security admins who hand deployment or Terraform work to agents on Google Cloud, or who manage those permissions.
What to do now First decide the permission scope you give the agent and the points where a human confirms policy changes. Then install the skills and test them.
Who needs to rethink permissions for IAM helper agent skills
If you have handed deployment to an agent, you need to decide again who opens which permissions, and how far. Think of a company badge. If a new hire gets a master badge that opens any door whenever they are blocked, security collapses. If they have to queue at the admin office every time, work stops. These skills tell the agent why a door will not open and even file the request for a temporary badge. The final stamp that changes the access rules stays with a human. Google Cloud designed it the same way, separating diagnosis from policy changes. This is only an analogy for the structure. As shown below, the actual risk-level criteria have not been published yet.
What changed: 4 skills and read-only MCP tools
In its official blog, Google Cloud explained that as agents create and deploy infrastructure on their own, permission problems appear more often and more quickly. Fixing permission errors by hand wears out developers and admins. Taking shortcuts lets agents receive excessive permissions and breaks the principle of least privilege. IAM helper is the answer. It is packaged to the open Agent Skills standard and, according to Google, works in Gemini CLI, Gemini Cloud Assist, ADK, Claude Code and Cursor.
| Skill name | What it does |
|---|---|
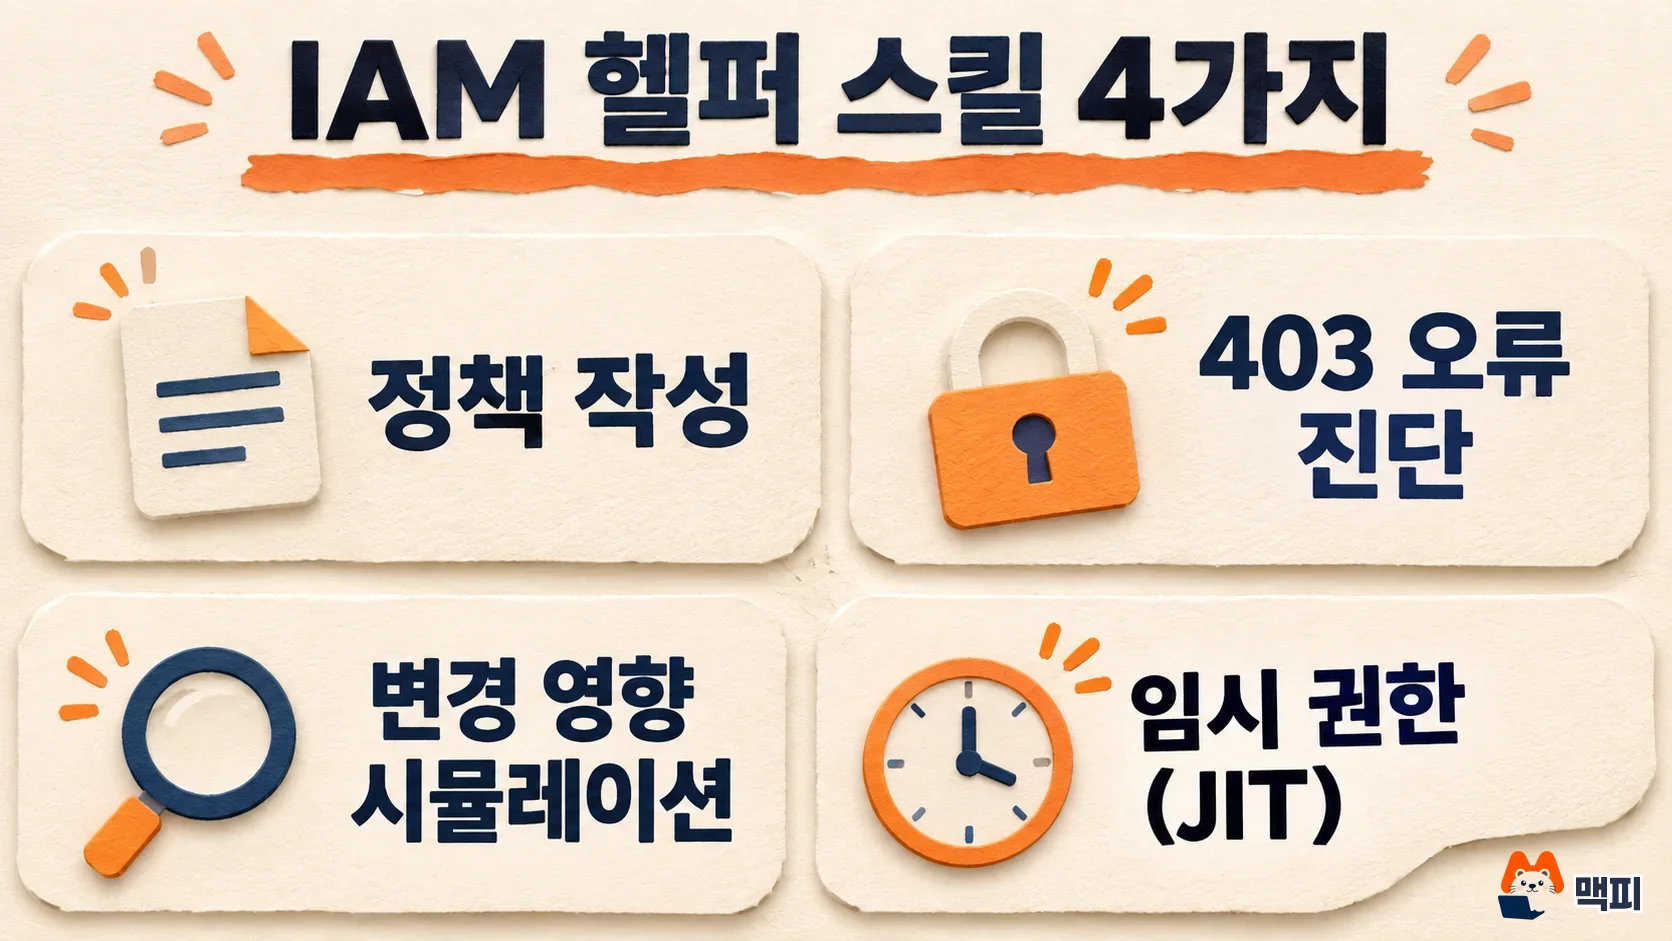
iam-helper-for-policy-management | Builds and validates IAM v1 allow rules and v2 deny rules from access requirements in JSON, YAML or Terraform format. It blocks allUsers public access and broad basic roles such as roles/owner and roles/editor before they are applied. |
iam-helper-for-troubleshooting | Finds the missing permission or blocking rule behind a 403 PERMISSION_DENIED error. The developer flow checks whether you can fix it yourself or drafts a request to send to an admin. The admin flow traces rules inherited through the organization, folders and projects. |
iam-helper-for-policy-simulator | Validates a policy change in 4 steps: plan, simulate, analyze and apply. It first checks the last 90 days of access logs to make sure existing traffic will not break. Google's Policy Simulator documentation also says it re-evaluates access attempts from the last 90 days against the current and proposed policies. |
iam-helper-for-privileged-access-management | Handles temporary access requests, approval and automatic revocation through Privileged Access Manager (PAM). Elevated access is audit-logged and time-limited. |
The tools the skills call directly are the IAM MCP tools on Google's managed MCP server. Google says these are read-only functions connected to Policy Troubleshooter, Policy Analyzer, Policy Simulator and the IAM v1 and v2 APIs. Teams do not need to build their own API wrappers. The agent finds and calls the tools, so it does not have to interpret long policy documents inside the prompt.
Does this apply to you: when agents handle your Google Cloud work
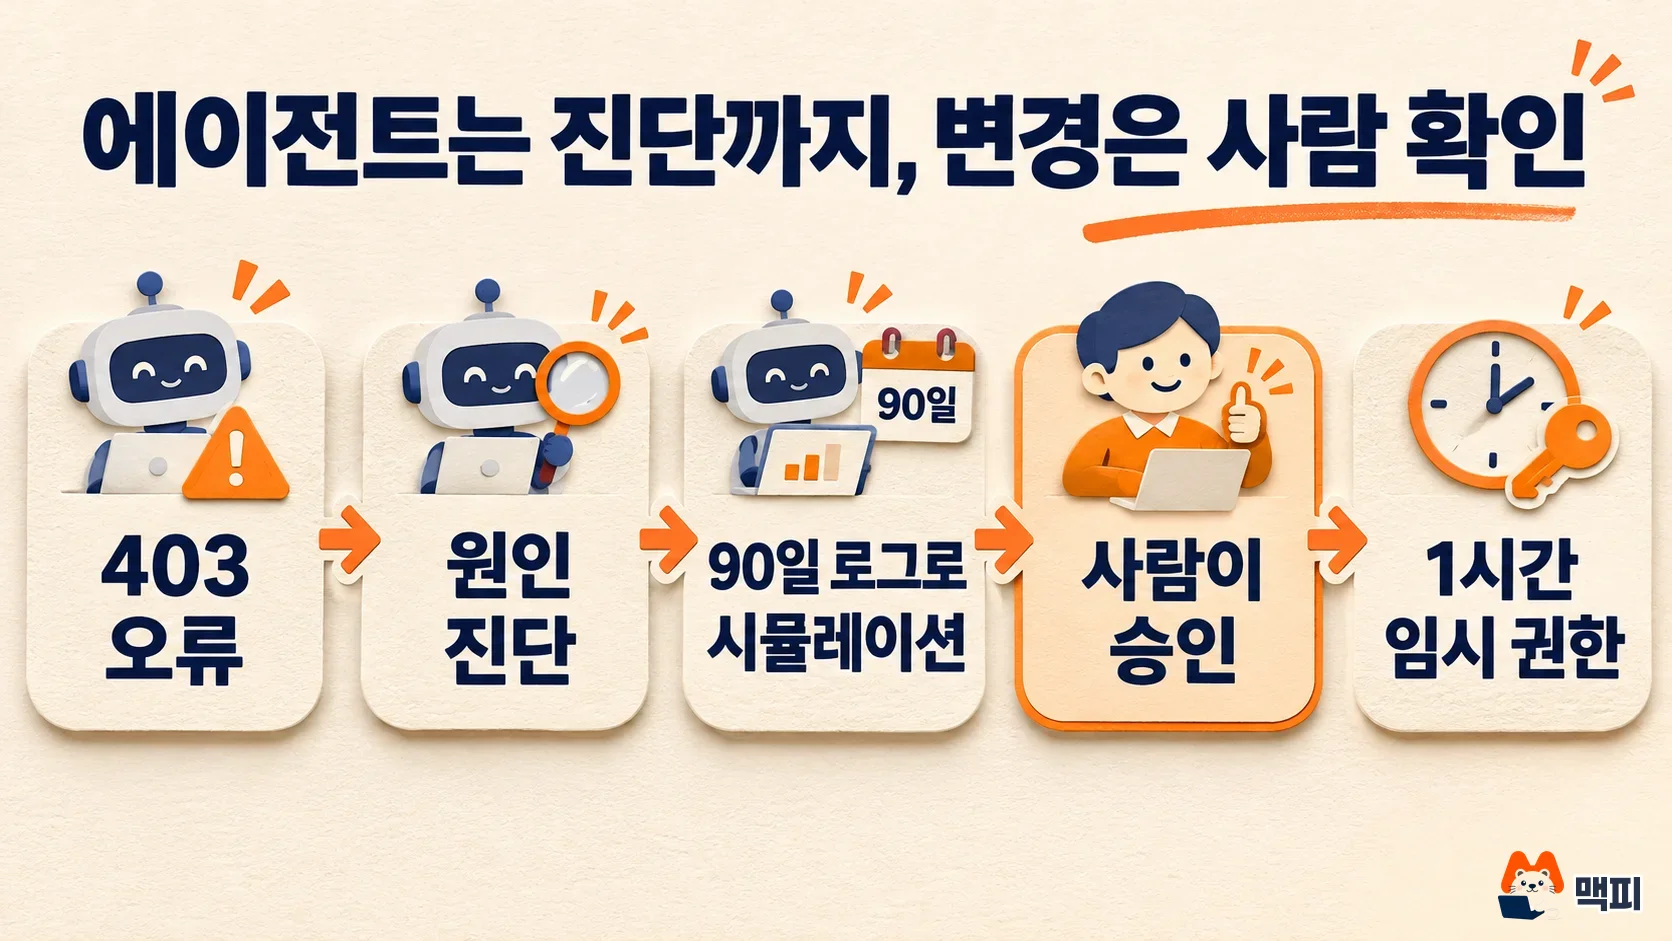
Google gave two usage scenarios. In the first, a developer's coding agent hits a 403 error during deployment. Instead of filing a ticket and waiting, it uses the diagnosis skill to find the missing Pub/Sub permission and the PAM skill to request a 1-hour temporary grant. In the second, an infrastructure agent is blocked by permissions in a deployment pipeline. Instead of failing the build, it drafts a least-privilege policy, checks the impact against 90 days of logs with the simulator, and then asks an admin for approval.
If your team does not use agents and manages permissions directly in the console, nothing changes right away. This is a connection layer for agents on top of IAM features you already use, so existing roles and policies are not changed automatically. When you connect other Google Cloud MCP tools to an agent, it is also worth checking the same principles first: human approval, narrow permissions and audit logs.
What to do now: set the permission scope before installing
If skills are new to you, you can start with What are Claude skills? How to build them with SKILL.md. The 4 skills sit in the skills/cloud/ folder of the Google Cloud Agent Skills catalog. According to the catalog instructions, you install them with npx skills add google/skills. When you run it, a screen lets you choose the skills to install, the target agent and the install scope (project or global).
- First review the roles granted to the service account the agent uses. To see how a broadly permitted agent account can spread to other resources, read How to check AI agent IAM lateral movement. Even if a skill asks for human confirmation, a path that bypasses the skill remains if the agent account holds a role that can edit IAM policies directly.
- At first, install only the troubleshooting skill (
iam-helper-for-troubleshooting) and the read-only tools, and check that it finds the real cause of a 403 error. - Turn on the policy management skill together with the simulator in a test project, and check that it asks a human for confirmation before changes.
- Use the PAM skill only after you decide who approves temporary access and how long it stays valid.
Check success in three ways. See whether the agent names the exact permission or rule behind a 403 error. See whether a policy change request stops at pending approval. See whether temporary access disappears after the set time. PAM events are recorded in Cloud Audit Logs, so also check that the request, approval and revocation records exist.
What to watch next
The blog does not say whether this is a preview or generally available, or whether it costs money. It also does not list which tools each skill supports or the MCP server address. Check these in the official IAM documentation before adopting. The blog only says that the standard for sending access policy changes to human confirmation follows a risk level that users can change. You will need to test which changes fall into which level. If you are new to agent development environments, start with How to use Google ADK to see the development kit where you attach skills.
Frequently asked questions
Can the IAM helper skills be used in Claude Code?
Google said in its official blog that they work in Gemini CLI, Gemini Cloud Assist, ADK, Claude Code and Cursor. You choose the target agent during installation.
Can the agent change permissions on its own?
According to the Google blog, diagnosis and simulation run automatically, but access policy changes stop for human confirmation depending on the risk level. The MCP tools themselves are read-only.
I only need to fix 403 errors. Do I have to install everything?
According to the Google catalog instructions, you can choose all skills or individual ones during installation. To find only the cause of 403 errors, install just the troubleshooting skill.
Found this useful? Share it
Latest posts
Kakao Share Thumbnail Not Showing? Here's the Fix (JavaScript SDK 2025)
Learn why Kakao Share thumbnails don't appear even with a valid imageUrl, and fix it using scrapImage to convert your URL into a KAGE CDN URL. Step-by-step guide.
How to Generate CRM User Manuals in 20 Minutes with Claude Code Sub-Agents
Learn how Claude Code sub-agents can analyze your CRM codebase and auto-generate user manuals and visual guidebooks in just 20 minutes. See the real-world results.
GEO Generative Engine Optimization: The Complete 2025 AI Marketing Strategy Guide
Learn what GEO (Generative Engine Optimization) is, how it differs from traditional SEO, and discover 5 proven AI marketing strategies to get cited by AI search engines in 2025.
Related projects
Get new posts by email
Insights on marketing, analytics, and dev, delivered to your inbox.